palaniappan p9 min
AWS Resource Hardening Quick Wins: DMS, OpenSearch, SageMaker, and Lambda Runtimes
Hardening quick wins: private DMS, OpenSearch encryption, SageMaker VPC-only, Lambda runtime EOL. July 2026 checklist.
Tagged
Hardening quick wins: private DMS, OpenSearch encryption, SageMaker VPC-only, Lambda runtime EOL. July 2026 checklist.
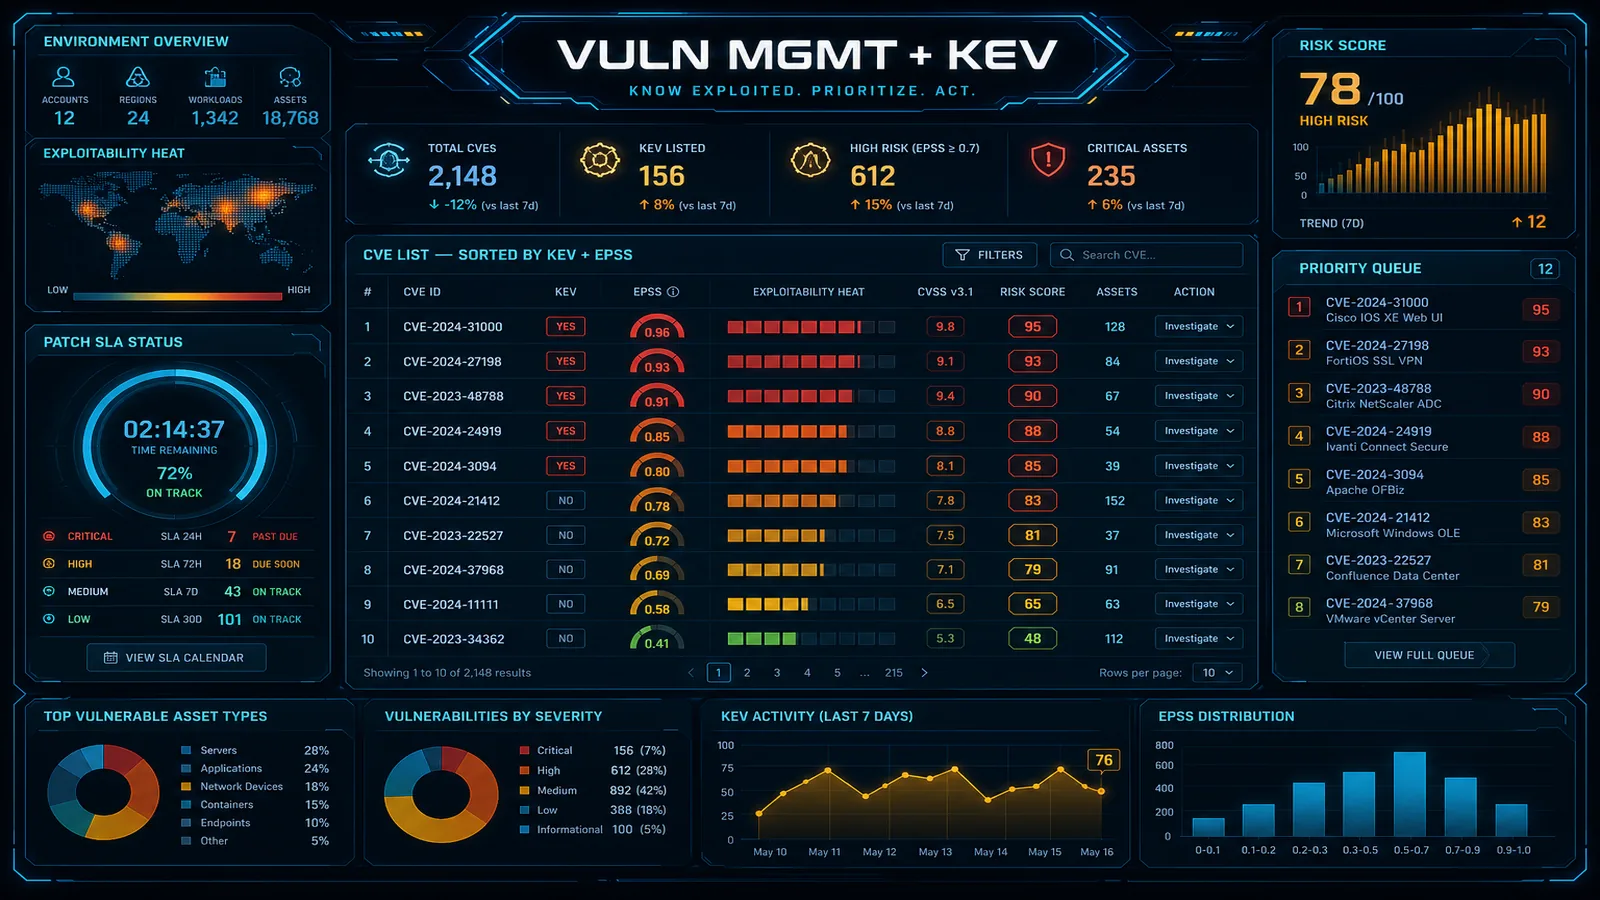
How to build a vulnerability management program that scales beyond CVE-counting. Inspector v2 deployment, CVSS + CISA KEV + reachability for risk-based prioritization, container and IaC scanning in CI/CD, and remediation SLAs that survive audits.
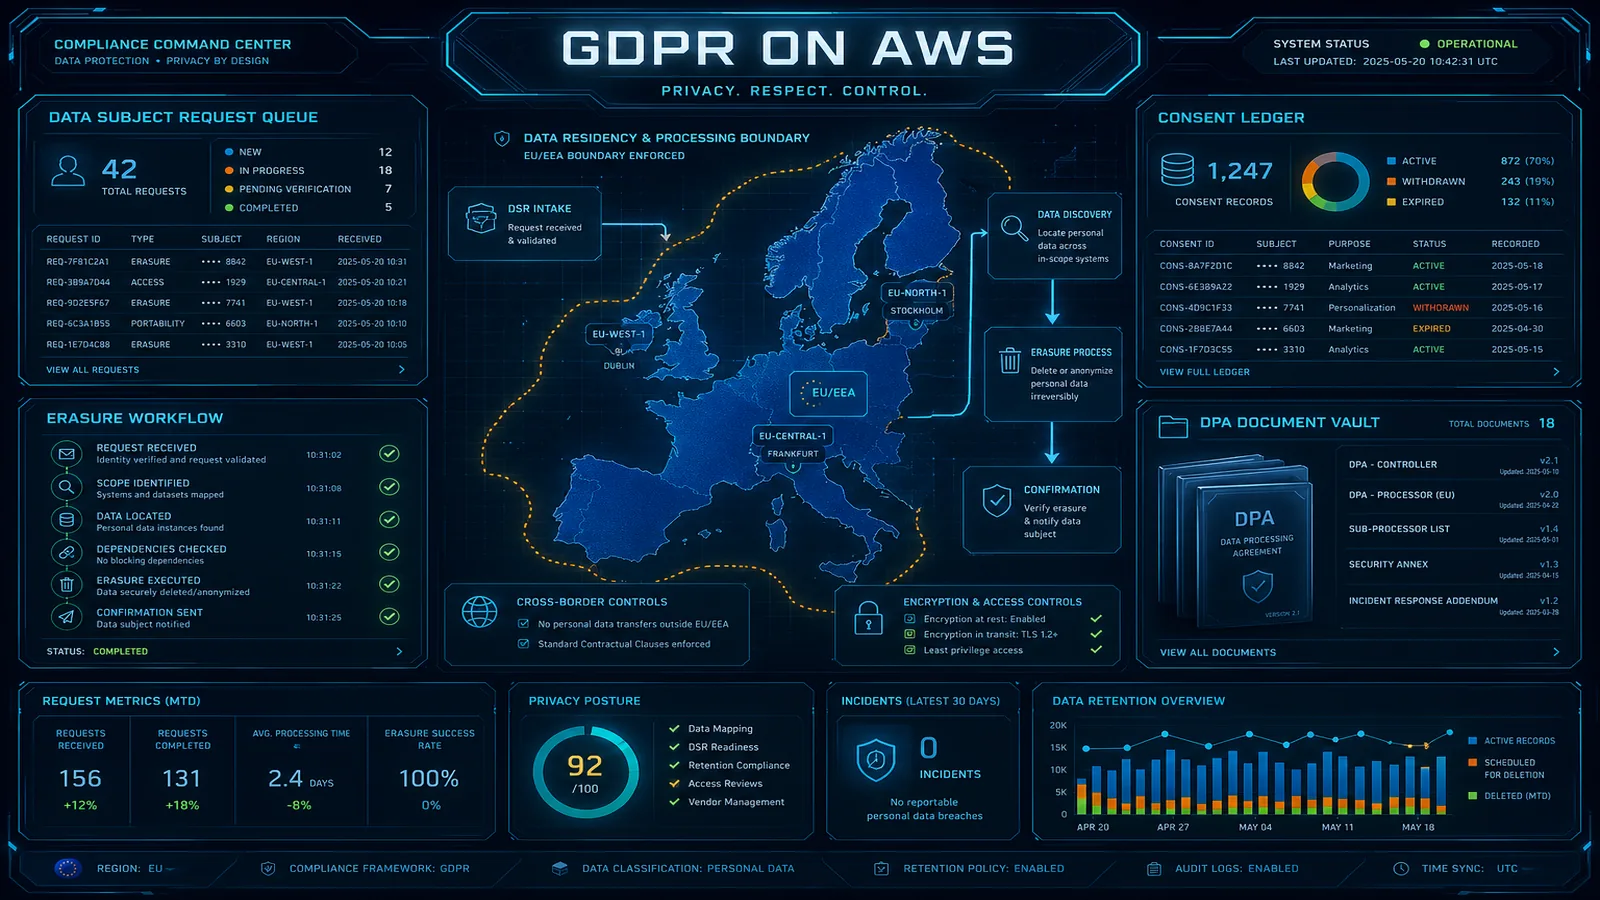
GDPR compliance on AWS for SaaS companies handling EU resident data. Region selection, the AWS DPA, data subject rights automation, RoPA documentation, breach notification, and the technical controls regulators expect.
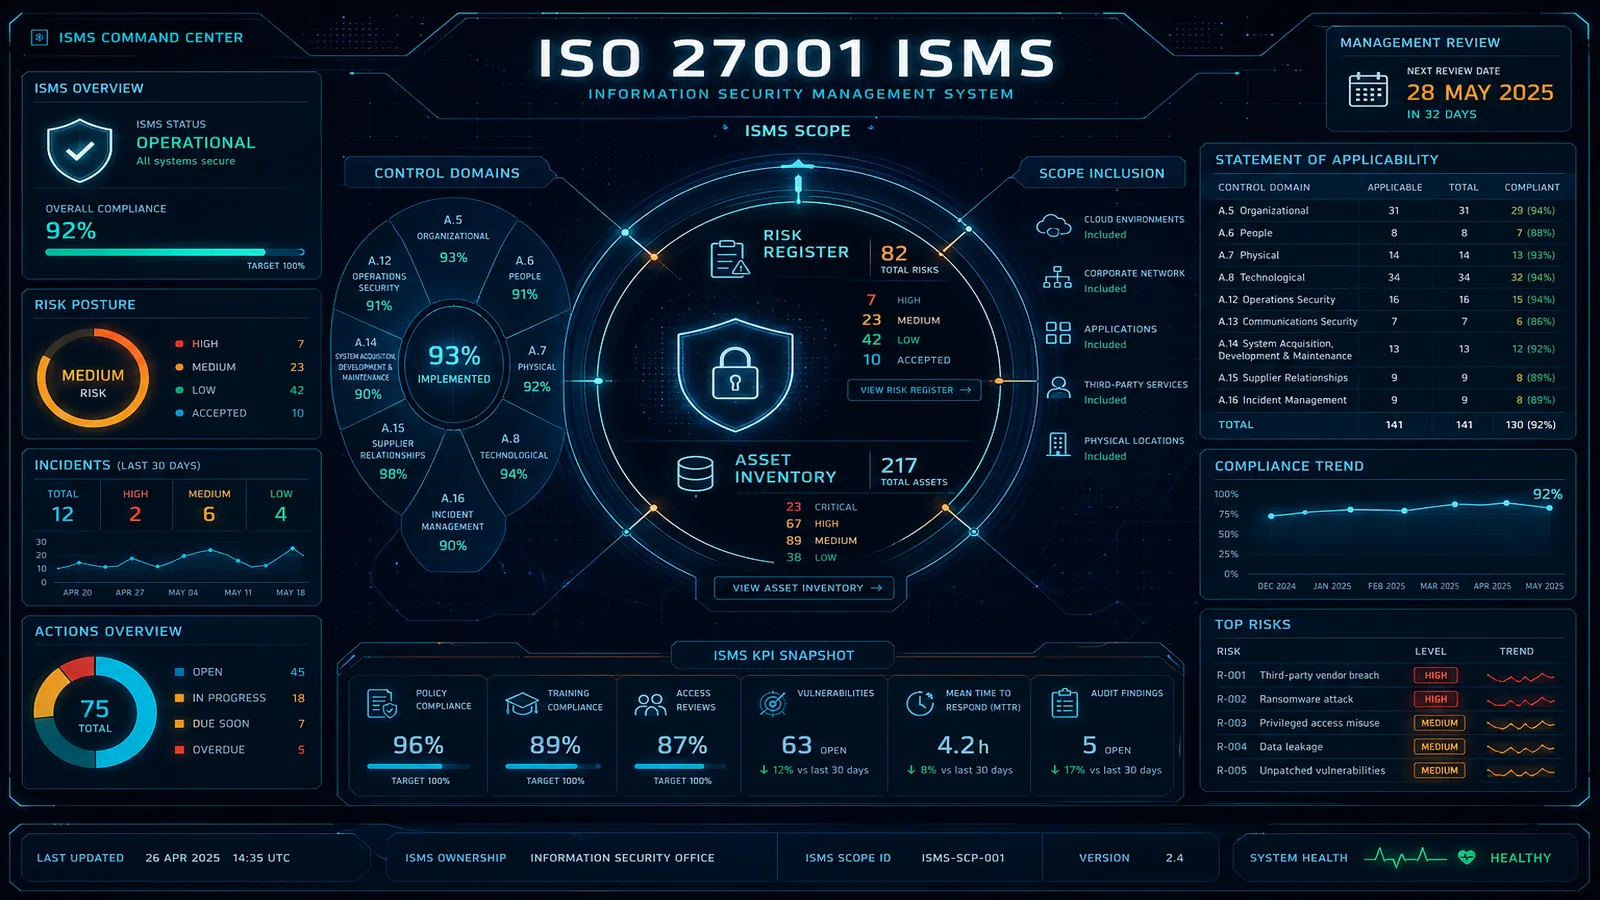
ISO 27001:2022 on AWS: ISMS scope, 93 Annex A mapping, Stage 1/2 evidence. July 2026 stage checklist.
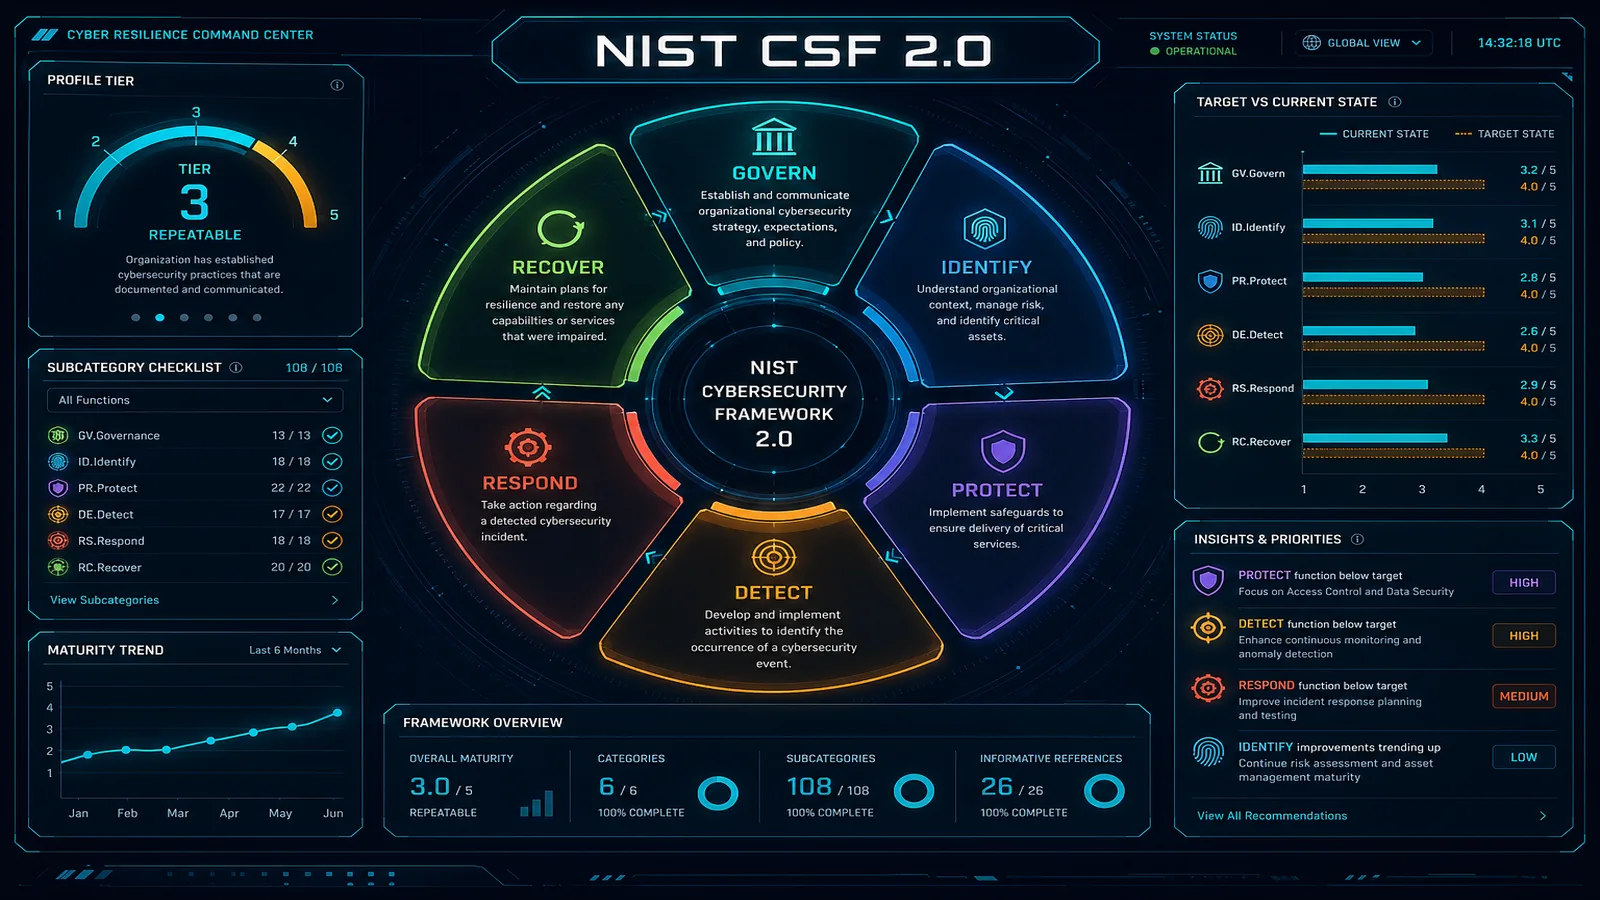
NIST CSF 2.0 on AWS: Govern + six functions, tiers, 800-53/171/CMMC. July 2026 Tier-3 checklist.
Most AWS security breaches aren't caused by AWS failures — they're caused by misconfiguration. Here are 10 concrete best practices to harden your AWS environment in 2026.
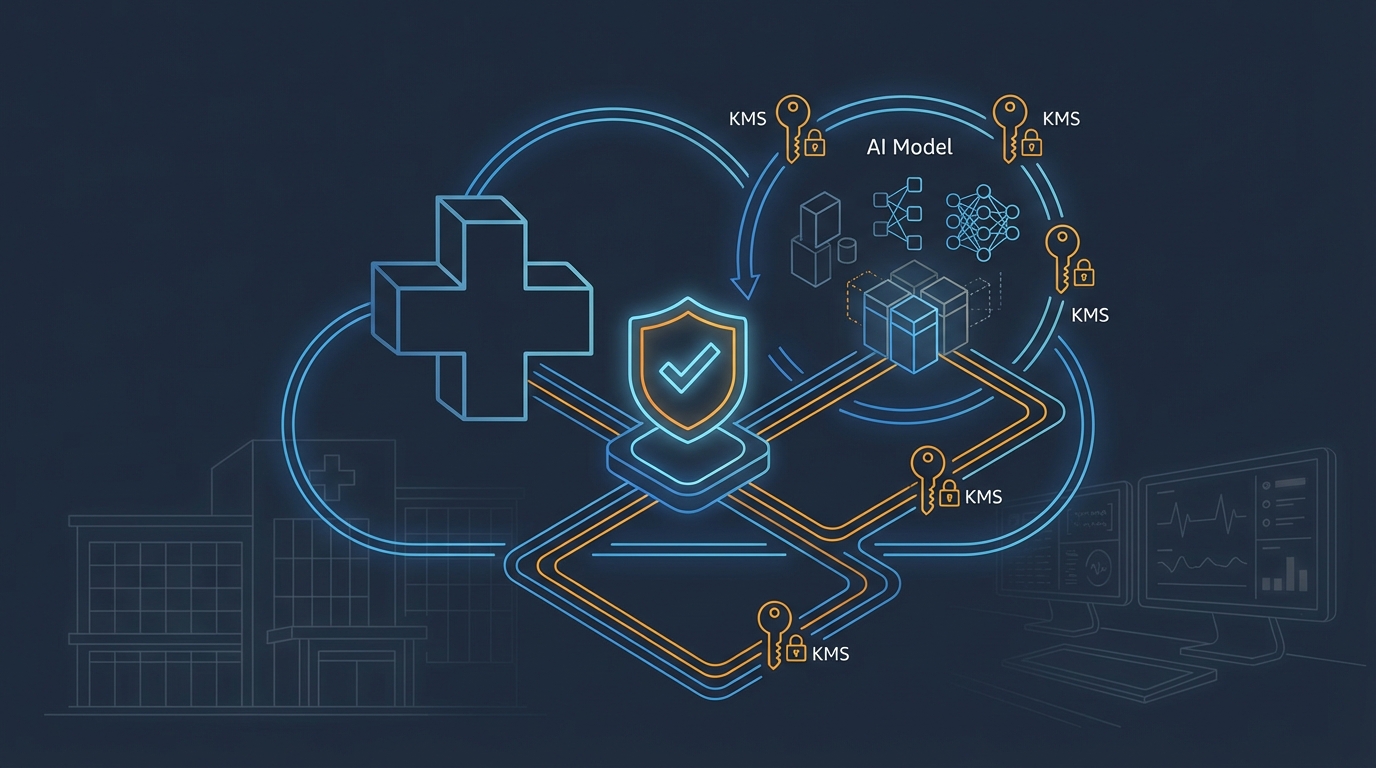
Production guide for HIPAA-compliant generative AI on AWS Bedrock — BAA scope, eligible models, Guardrails for PHI redaction, Knowledge Bases for RAG over clinical data, VPC isolation, and the audit evidence package OCR investigators expect.
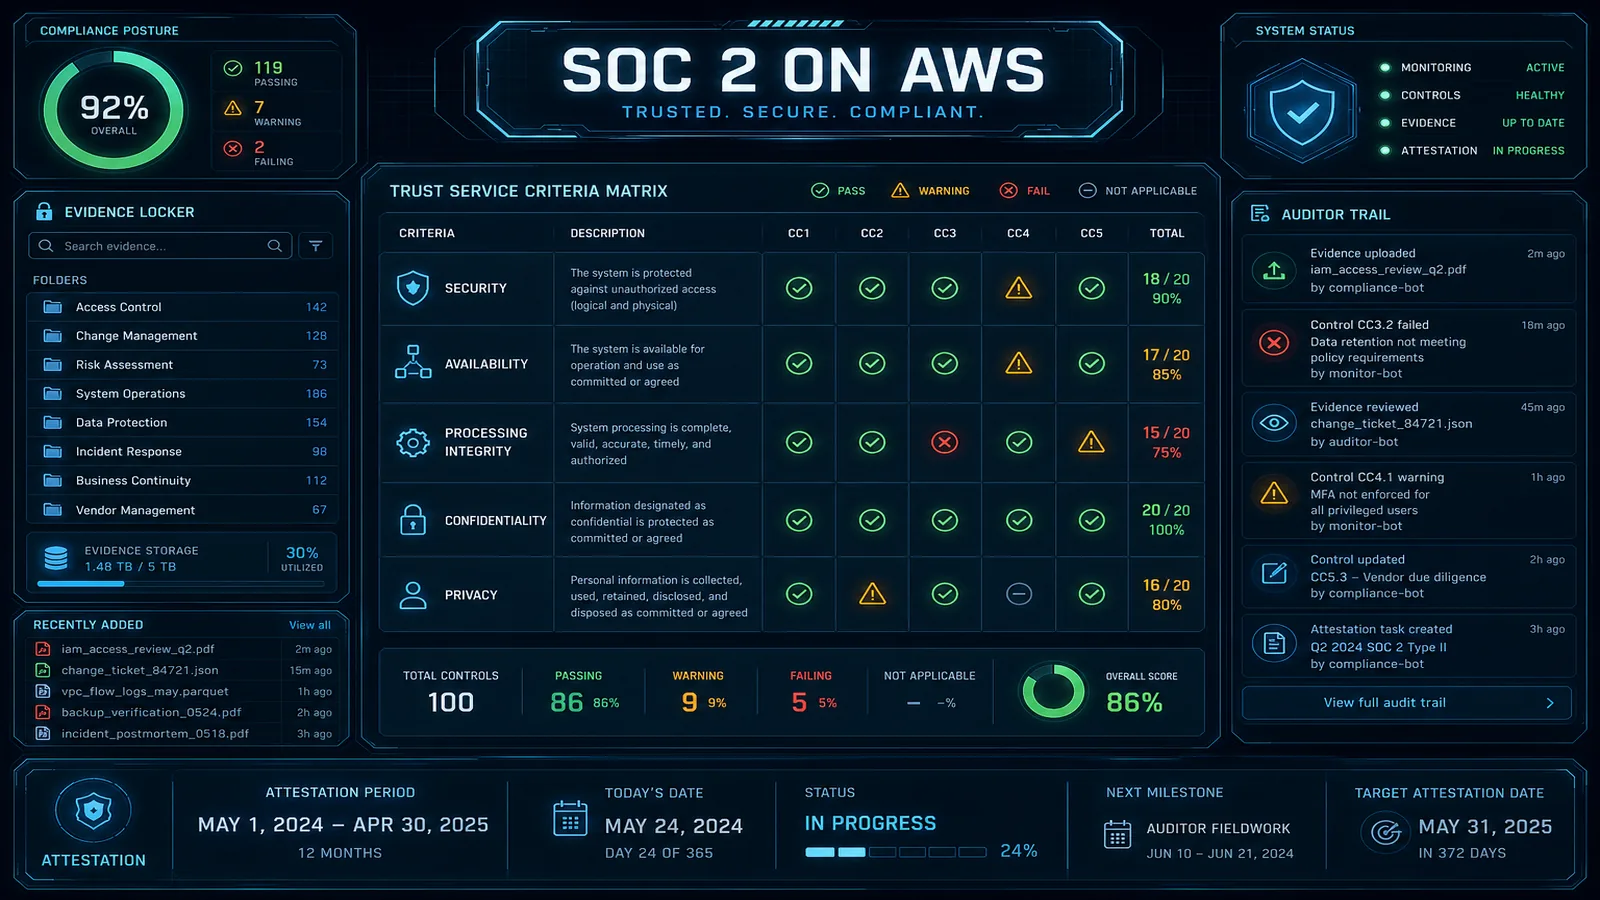
SOC 2 Type II certification proves your controls are effective over 6-12 months. This guide covers the compliance roadmap, AWS security controls, documentation requirements, and audit preparation for 2026 certification.
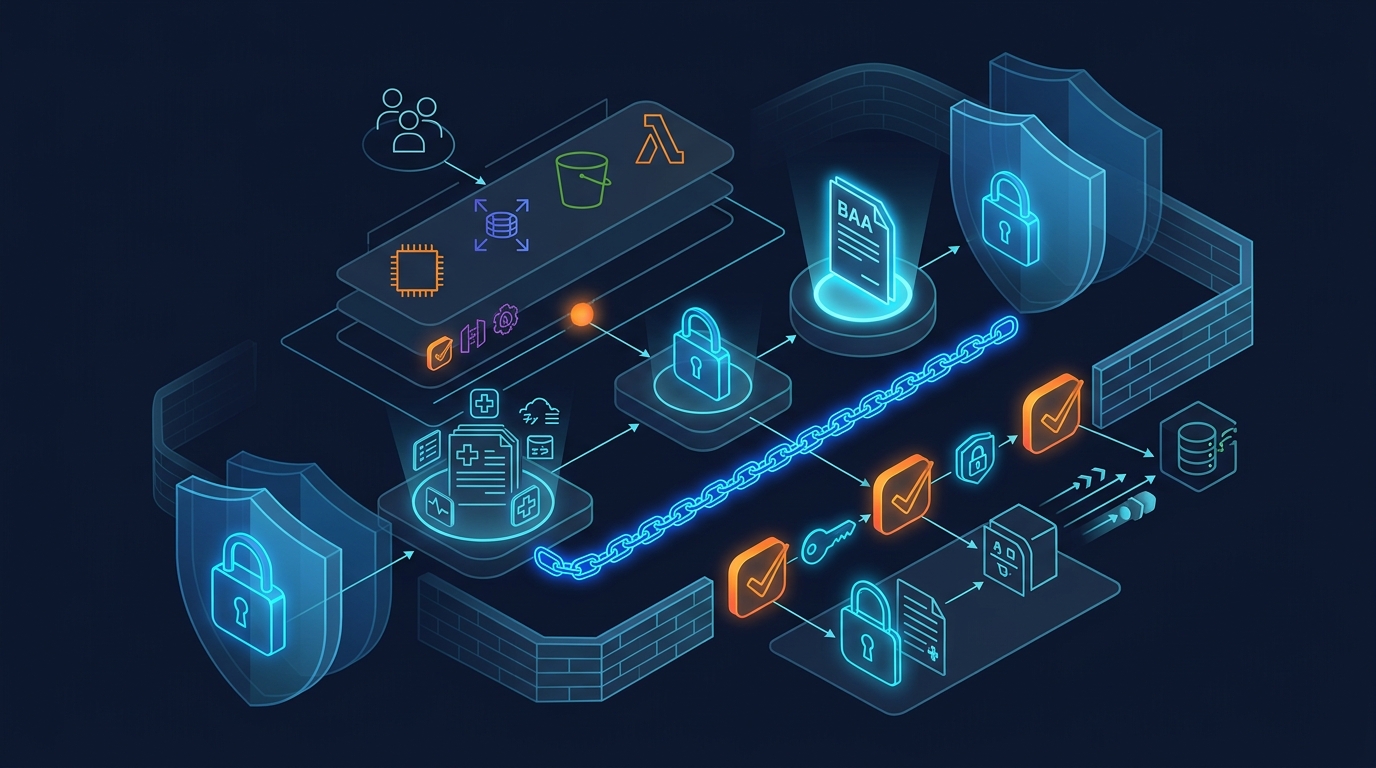
HIPAA on AWS build guide: BAA via Artifact, eligible services, KMS/VPC/RDS/S3 patterns. July 2026 engineering checklist.
AWS Control Tower automates multi-account management — setting up guardrails, enforcing compliance policies, and centralizing billing. This guide covers setup, customization, and production governance patterns.
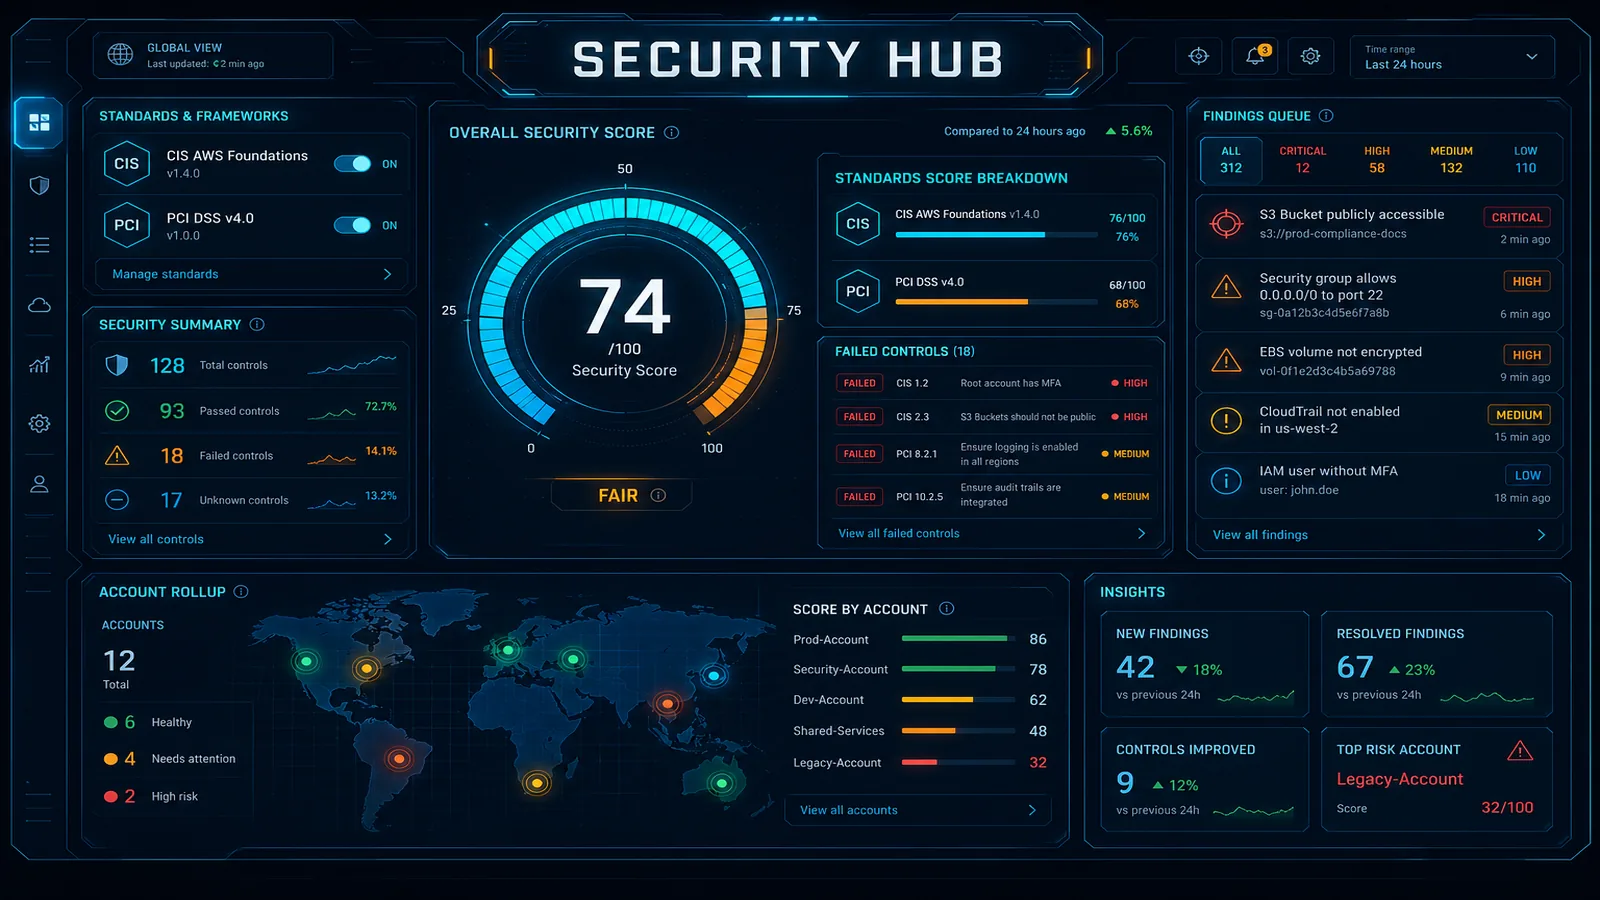
AWS Security Hub aggregates security findings from 200+ sources and, as of Jul 14 2026, includes AI inventory for org-wide AI assets. This guide covers setup, compliance standards, AI inventory, automated remediation, and a compliance dashboard without hiring a SOC team.
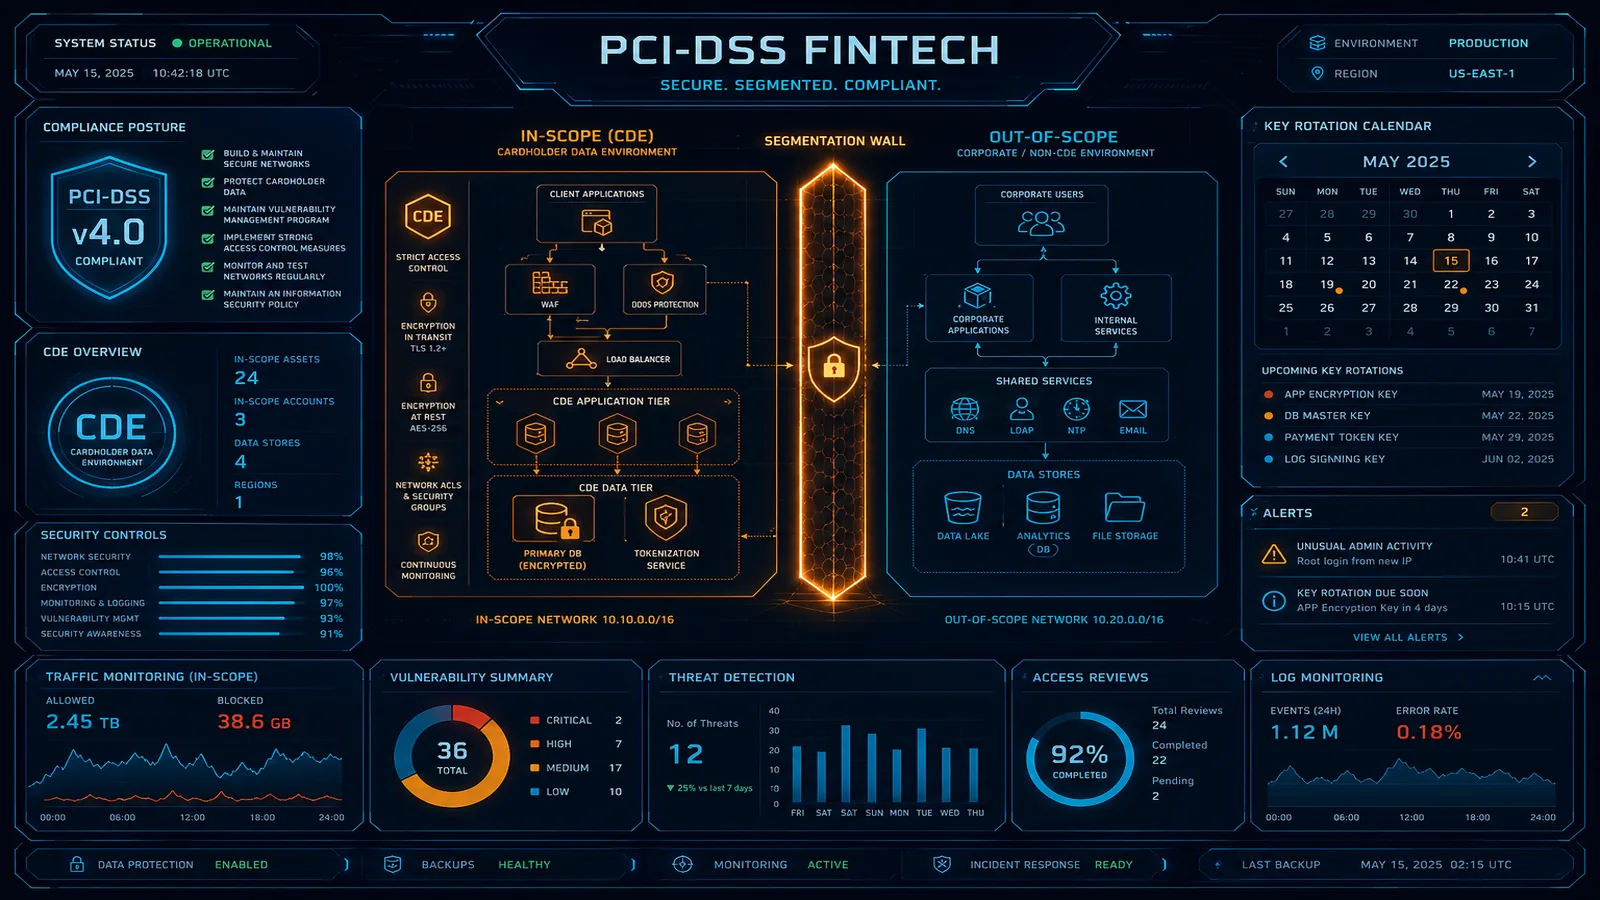
A practical architecture guide for PCI DSS compliance on AWS — CDE scoping, the 12 requirements mapped to AWS services, network design, encryption, logging, and audit readiness for payment-processing applications.